Missing security header: Content-Security-Policy

URL: https://launcher.arcblock.io/en
evidence: Response does not include the HTTP Content-Security-Policy security header or meta tag Request / Response
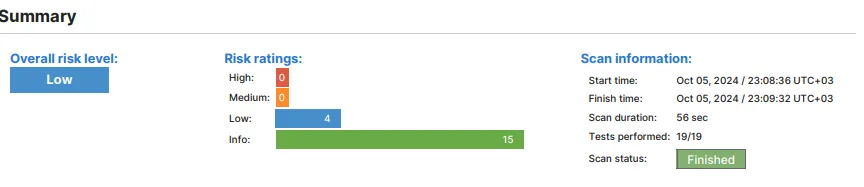
Description: This happening when i scanning and do penetration test to the alt domain on arcblock.io which is https://launcher.arcblock.io/en
Risk description: The risk is that if the target application is vulnerable to XSS, lack of this header makes it easily exploitable by attackers.
Recommendation: CONFIRMED 1 / 5 Configure the Content-Security-Header to be sent with each HTTP response in order to apply the specific policies needed by the application.
References: https://cheatsheetseries.owasp.org/cheatsheets/Content_Security_Policy_Cheat_Sheet.html https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Content-Security-Policy
Classification: CWE : CWE-693 OWASP Top 10 - 2017 : A6 - Security Misconfiguration OWASP Top 10 - 2021 : A5 - Security Misconfiguration
1 条回复
Hi, this is a known issue, and there is an improve in progress, will release when ready.