DID Wallet Allows Unlimited Invalid Password Attempts

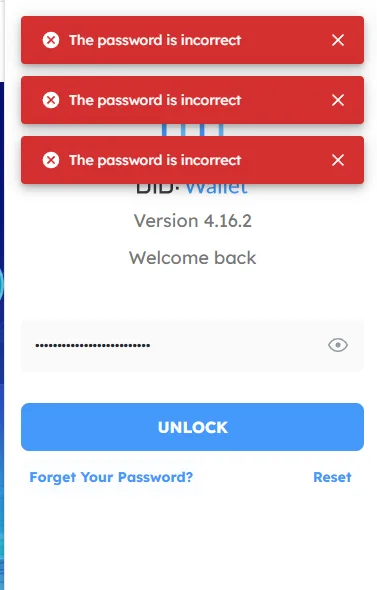
On the DID Wallet, users can repeatedly attempt to log in with an invalid password without any restriction or security control. The system does not enforce a lockout, cooldown, or rate-limiting after multiple failed attempts, leaving it vulnerable to brute force attacks.
Steps to Reproduce:
- Open DID Wallet.
- Enter an incorrect password.
- Click Login → system responds with "Invalid password."
- Repeat the process indefinitely.
- Observe that no account lockout or delay occurs.
Expected Result: After several failed password attempts (e.g., 5), the wallet should:
- Temporarily lock the account, or
- Introduce a cooldown/delay before retry, or
- Trigger additional verification (e.g., CAPTCHA, 2FA).
Actual Result: The system allows unlimited invalid password attempts without any restriction or delay.
Bug Description: The DID Wallet’s login flow lacks brute force protection. Attackers can automate unlimited password attempts until the correct one is found, significantly weakening wallet security.
Suggested Fix:
- Implement account lockout after 5–10 invalid attempts.
- Add progressive delays (e.g., exponential backoff) after repeated failures.
- Consider integrating CAPTCHA or 2FA prompt after multiple invalid logins.
- Provide secure error handling (avoid detailed error messages).
Priority: 🚨 Critical – Must fix urgently to protect user accounts and digital assets.
1 reply
你好,感谢您的反馈,我们会在后续钱包版本中考虑增加该改进。